About

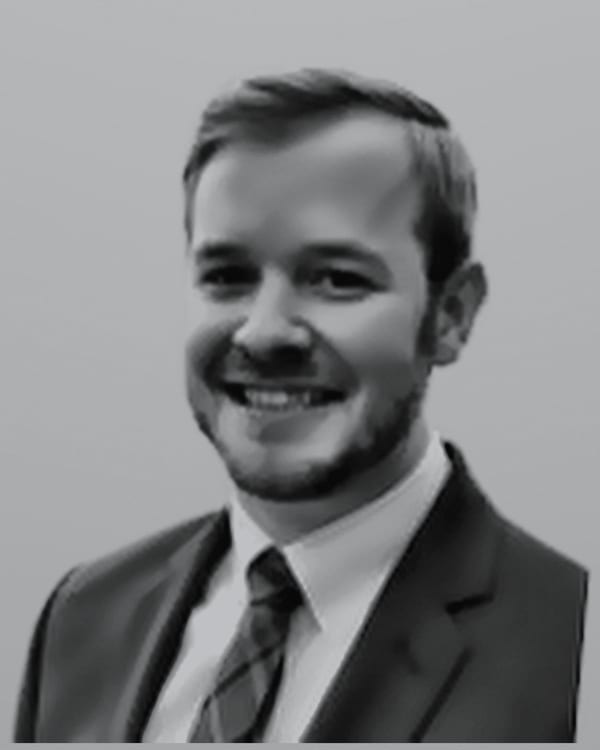
Gray Faulkner

Faulkner Governance Risk & Compliance, Austin, Texas. Years deciding what passes inspection. Now on your side of the table.

Gray Faulkner
Gray Faulkner, CISA, CCSK

The short version

Gray spent a career in Big Four and national firm risk practices: internal audit, SOX and ICFR, and technology risk engagements for public and high growth technology companies, advising CFOs, controllers, heads of internal audit, CIOs and audit committees. At the national firm Gray built and led the Austin risk consulting practice and directed global delivery teams for public and pre IPO clients.

The standard the work is built to comes from the other side of the table. Gray defended audit scope, methodology, evidence and conclusions through annual PCAOB inspections, and led the internal quality inspections across engagement teams. Evidence prepared the way an inspector expects to find it is the whole method.

Gray holds the CISA and the CCSK, served as Vice President and board member of the ISACA Austin Chapter, and studied accounting and information systems at Texas A&M University. Faulkner Governance Risk & Compliance is based in Austin, Texas, and works remote or on site nationwide.

Hiring Gray looks like this. A two hour scoping call, then a short letter that names the deliverables, the dates and the fee. Gray does the work, senior from the first call to the retest, with no handoff to junior staff; where a scope needs more hands they are added only with your written consent, and Gray stays on the work. Every week, one page: what was done, what is blocked, and what you need to decide. If your external auditor writes up a deficiency on a control we documented and tested, we remediate it at no charge.

I

Curriculum vitae

  • 2026 to presentOwner, Faulkner Governance Risk & Compliance, Austin

    Advisory work for public companies, companies heading to an IPO and PE backed companies: SOX and ICFR readiness, control documentation and testing, deficiency remediation, PCAOB grade testing for management, and a fractional SOX compliance lead. Third party and vendor contract risk for financial services and technology clients, including vendor agreement frameworks built to regulatory requirements such as GLBA and NCUA Part 748.

  • 2019 to 2020Vice President and board member, ISACA Austin Chapter

    Elected chapter leadership for the professional body for information systems audit, governance, risk and security: programming, sponsor relationships and professional development for the Austin market.

  • 2017 to 2026Director, risk consulting, a national firm, Austin

    Advanced from supervisor to director. Built and led the Austin risk consulting practice and directed global delivery teams for public and pre IPO clients. Led internal audit, SOX and ICFR, and technology risk engagements as an executive level advisor to CFOs, controllers, heads of internal audit, CIOs and audit committees. Defended audit scope, methodology, evidence and conclusions through annual PCAOB inspections with zero comments, and led the internal quality inspections across engagement teams.

  • 2013 to 2017Advisory associate to senior associate, a Big Four firm, Houston and Austin

    IT audit and risk advisory in support of financial statement audits, SOX readiness, IT governance and transformation programs. Fieldwork over ERP platforms, application controls and system implementations alongside financial statement audit teams. The firm chairman’s award for high performance, 2015.

Record current as of September 25, 2026.

II

Education and credentials

  • 2012Texas A&M University, Mays Business School

    M.S. in Management Information Systems and B.B.A. in Accounting, through the Professional Program in Accounting.

  • ISACA, since 2015Certified Information Systems Auditor (CISA)

  • Cloud Security Alliance, 2026Certificate of Cloud Security Knowledge (CCSK)

III

What Gray is asked about

  • Audit committee reporting
  • Public company internal audit, SOX and ICFR
  • PCAOB inspection readiness
  • Technology risk and integrated audits
  • ITGCs, application controls, logical access, segregation of duties, change management

Also asked about

  • Cloud platform risk: AWS, GCP, configuration review, IAM architecture
  • AI governance: model risk for generative and agentic AI, AI enabled audit tooling
  • Third party and vendor contract risk
  • Fintech, financial services and digital platform risk
IV

Off the clock

Gray lives in Spicewood, west of Austin, with his wife, his high school sweetheart, whom he married in 2011, and their three children. Weekends go to the water when the weather allows and to three children’s schedules when it does not, and to the list of things around the house that a person who tests controls for a living ought to be better at finishing.

Three children have taught him more about this work than any framework has. They ask why until the answer is plain, they can tell when an adult is bluffing, and they remember a promise long after the adult has forgotten making it. Clients get the same treatment he tries to give at home: an answer in plain words, a straight “I do not know yet” when that is the truth, and a date that means the date.

He came to this side of the table because he remembers the other one. He has been in the room when a controller who did everything right still got a finding, and he has watched capable people dread one season of the year because of how they were treated during it. The people he works with are busy, competent and tired of being audited. The job, as he sees it, is to make their auditor’s year uneventful, and to make sure that when the audit committee hears about the controls, the person who built them gets the credit.

He likes the people in this profession. He gave two years to the ISACA Austin Chapter as a board member and vice president because the auditors and security people in this city are generous with what they know, and he tries to be the same. Ask him a question and he will answer it whether or not there is an engagement attached. He would rather be the person you call before there is a problem than the one you call after.

None of this is on the capability statement, and none of it needs to be. It is here because a client hires a person before they hire a firm, and they deserve to know a little about him before the first call.

Start with a scoping call

Send the date on your audit calendar and a sentence on what is coming up.